Product Development Approach
VLSI
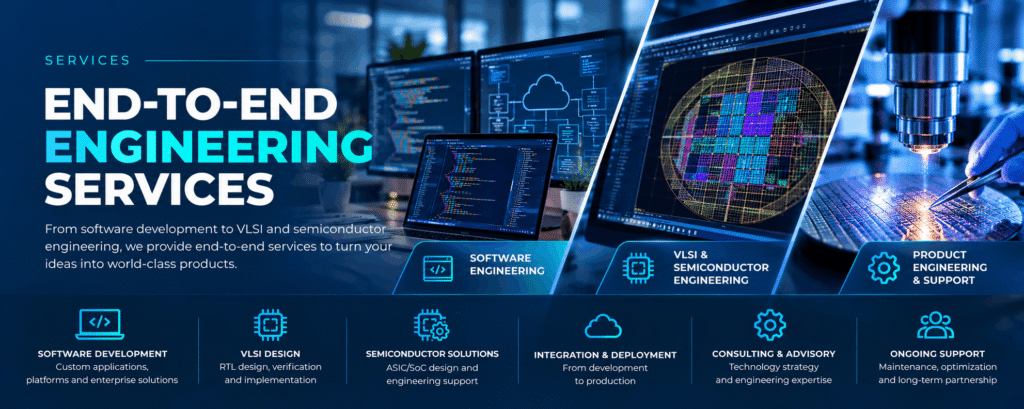
RTL Design: Clean, synthesizable Verilog/VHDL code for complex digital blocks and high-speed interfaces.
Functional Verification: UVM-based testbenches with 95%+ coverage for design confidence before synthesis.
FPGA Prototyping: Rapid system validation using Xilinx and Intel FPGA platforms for pre-silicon testing.
Backend Design & Sign-Off
Physical Design: Full flow including floorplanning, CTS, place & route, and timing closure.
PPA Optimization: Power, performance, and area tuning using multi-Vt, clock gating, and low-power techniques.
Physical Verification: DRC, LVS, ERC, and IR/EM sign-off for tape-out readiness.
DFT Implementation: Scan insertion, MBIST, boundary scan, and ATPG for high test coverage.
Custom Application Development
ArsenaliT provides the resources and expertise needed to build pragmatic solutions tailored for each client’s unique environment. BeyondOI focuses on providing end-to-end implementation and support services in the areas of Rich Internet Applications, Business Workflow Applications, Web2Print Solutions, Mobile Applications Development, Social Community Solutions and Solutions on the Cloud.
Our team has extensive project lifecycle management experience delivering projects on both open source and commercial platforms. BeyondOI has always been a pioneer in adapting cutting edge technology trends for building custom applications for its clients. Considering the tradeoff that is required between choosing an Off- The – Shelf product and custom application development, BeyondOI adopts rapid application development framework by executing the development cycle over series of frameworks available on both OSS and Commercial platform.
Mobile Application Development
Architecture Review and Assessment
ArsenaliT Architecture Assessment offers a complete architectural analysis and assessment of your IT application, focusing on Quality of Service (QOS) parameters such as scalability, performance, interoperability, usability, Security and much more.
These parameters are derived from the ISO 9126 QOS framework and the analysis uses SEI’s Architecture Trade-off Analysis Method (ATAM).
We also study the existing system architecture to identify their current flaws, fit gap analysis, database errors, defects, etc., and provide a solution summary to overcome the identified issues.Â
Web Application Security – OWASP
We already have a very good experience on applying web application securities based on the OWASP standard. Our nature way of writing code will fulfil most of the security measures like Client & Server side validations to prevent from wrong data’s or pre check before our business logic implementation, error/exception handlings to stop unnecessary way to hacker to know about our background process like database tables/Pojo/class etc.., disabling browser cache to avoid history after his/her session logouts, CSRF to avoid cross side scripting or stops script injection, sanitization to check the malicious code/data, session fixation to avoid session hacking while login and logout, SQL injection to prevent stealing data, brute force attacks to stop password hacking, salted hash password to avoid man in the middle to see the password in clear text, autocomplete to avoid storing your valuable data like password/credit card number/contact in the client side, encryption/decryption is used if you want to do it by own or rather than using https to deal with 3rd party or web services, One way hashing like hmac to create signatures to check the incoming data’s are not tampered etc..
We are ensuring that, we can prevent from top 10 web app hackings and also we can do all other security measure setups like https/firewall etc…